The typical organisation takes 43 days to fully fix a known exploited flaw, and attackers often move sooner. Here is how to protect yourself in the gap.
Picture a Monday morning. An advisory lands for the VPN gateway that sits at the edge of your network. By Wednesday the patch is tested and approved, and it goes on the calendar for the weekend maintenance window.
It feels like a well-run process, and it is. The trouble is that attackers may not be waiting for the weekend. In October 2026, a flaw in Ivanti Connect Secure was being exploited in the first days of the month, ahead of CISA’s public alert on 13 October.
So the question for security leaders is changing. It used to be how fast we patch. Increasingly it is what an attacker can reach while we wait.
What We Mean by the Patch Gap
The patch gap is the stretch of time between attackers starting to use a flaw and you finishing the fix. Three clocks decide how long it lasts and how much it hurts: how fast attackers move, how fast you fix, and how fast an intruder can take your data once inside.
Most board reports show only the second clock, as a patching percentage. The other two rarely make it onto a slide, and they are the ones that decide what a delay costs.
The Numbers Are Moving the Wrong Way
The latest research tells a consistent story.
- 31%Using a known flaw is now the most common way breaches begin, at 31% in Verizon’s 2026 Data Breach Investigations Report. A year earlier it was 20%.
- 43 daysThe typical organisation now takes 43 days to fully fix a known exploited flaw, up from 32. Only 26% of those flaws were fully fixed, down from 38%.
- 31 daysRecorded Future found that in the first half of 2026 the typical flaw was being exploited 31 days after disclosure. And 38% were exploited within a week of disclosure, or before it.
- 36 daysInterlock, a ransomware group, was exploiting a flaw in Cisco’s firewall management software about 36 days before Cisco disclosed it.
These numbers come from different studies, so treat them as a sense of scale and not a forecast for your own estate. The direction is still clear. Attackers are using known flaws more often, and fixes are taking longer.
Doing the Sums
Take a critical flaw in a device that faces the internet, and use those typical figures.
How long you are exposed, in days
Each bar runs from the first attack to the typical fix at day 43. Illustrations built from the figures above.
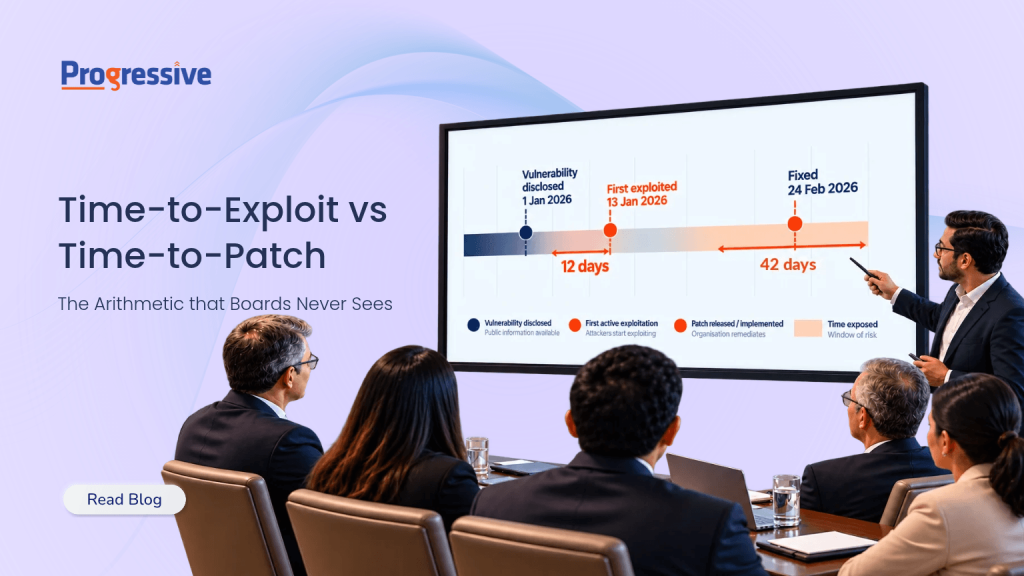
- If attackers move at the typical 31 days and you fix at the typical 43, you are exposed for about 12 days.
- If they move within a week, as they did for 38% of exploited flaws, the same fix time leaves you exposed for about 36 days.
- If they move before disclosure, as with the Cisco flaw, it is about 79 days from the first attack to your finished fix. That is 36 days plus 43.
These are illustrations, not measurements, and your own numbers will differ. The point is that exposure is a number a board can understand, and it deserves the same airtime as the patching percentage.
There is a third clock to keep in mind. Unit 42 found that in the fastest quarter of intrusions, attackers had taken data within 1.2 hours. A window measured in days cannot be covered by watching alone. You also need to limit what an attacker can reach in the first place.
What You Can Do While You Wait
Hardening does not replace patching. Think of it as making the building harder to move around in while the repair crew is on its way.
Keep Admin Doors Off the Internet
The admin screens of firewalls, VPN gateways and management consoles are what attackers go for first. Cisco said its flaw was less exposed where the management interface had no public internet access. If someone needs remote access, send it through an approved route.
Limit Who Can Administer
Put administration behind a jump host with multi-factor authentication, on its own network segment, and allow only named people and devices. Switch off services you do not use.
Retire What Cannot Be Patched
Devices that no longer receive updates cannot be fixed. VulnCheck found that about 42.5% of the 181 edge device flaws it added to its known exploited list in 2025 affected products that were end-of-life or probably end-of-life.
Keep Logs Somewhere Safe
Attackers can tamper with the logs on a device they have taken over. Volexity saw this in the Ivanti attacks. Sending logs to a separate platform means investigators still have a record they can trust.
Make It Stay Hardened
A secure configuration only helps while it stays in place. Unit 42 found that preventable gaps and inconsistently applied controls played a part in more than 90% of the incidents it investigated. Baselines based on CIS or NIST guidance, golden images (a pre-approved, hardened build for every new system) and drift detection (an alert when a setting moves away from the baseline) stop settings slipping quietly.
Where to Start
Start with whatever faces the internet, because that is where exploitation often begins. Here are five questions to put to your team this week.
- What can the internet see?List the internet-facing devices and any admin interface that can be reached from outside.
- How long do we really take to fix?Work out the typical time to fully fix a known exploited flaw, and how many get fully fixed.
- What protects us on day one?For a flaw attackers use before it is disclosed, decide the stopgap, such as restricting access.
- Are our devices still set the way we decided?Compare current settings with the agreed baseline and look for drift.
- Who can edit our logs?Make sure device logs reach a platform an attacker cannot alter.
Give each control an owner, a way to approve exceptions and a review date. An exception with no end date can quietly become permanent.
How to Know It Is Working
Judge a hardening programme by what changes. These measures help:
- The typical time to fully fix known exploited flaws.
- The share of those flaws that get fully fixed.
- The number of internet-facing admin interfaces.
- The number of end-of-life devices still in service.
- Configuration drift findings, and how long they stay open.
Track these by how critical each system is. A quick patch rate on low-risk systems says little about the devices attackers go for first.
The Takeaway
Patching speed is easy to report, so it gets the attention. Exposure is harder to see, and it is closer to what attackers actually experience.
A board that asks only how fast we patch is looking at one clock of three. The better question to take into your next meeting is what an attacker can reach in the days before the fix lands, and who has checked.
How Progressive Techserve Helps
Our Security Hardening and Baselining service applies CIS and NIST baselines, golden images and drift control across your environment. We can deliver it as a project to set the baseline, or as a managed service that keeps it in place, alongside our identity, cloud, and detection and response services.
We usually start by looking at what you already have: which devices face the internet, where settings differ from the baseline and which controls can be enforced without disrupting operations.
If you would like to reduce your exposure while patches are still on the way, talk to us about your security hardening and baselining priorities.
Contact Progressive TechserveWrite to solutions@progressive.in
Frequently Asked Questions
What is the difference between patching and hardening?
Patching fixes a specific flaw. Hardening makes a system harder to attack by removing unnecessary exposure, services and permissions, and by keeping settings in line with an agreed baseline. The two work together.
What is a security baseline?
A security baseline is an agreed secure configuration for a type of system, usually based on CIS Benchmarks or NIST guidance. Real configurations are checked against it.
What is configuration drift?
Drift is what happens when a system’s settings move away from the approved baseline over time, through changes, exceptions or manual fixes. It can weaken controls that were once in place.
Can hardening protect an unpatched device?
It can reduce exposure and limit what an attacker can reach, but it does not remove the flaw. Patching and monitoring still matter.